Bonsoir achille-myrmidon,
Plusieurs infections sur votre ordinateur.
Désinstaller via Panneau de configuration >> Programmes et Fonctionnalités (si présents) :
Java 7 Update 45
Java(TM) 6 Update 14
Désinstalle aussi la vieille version de Malwarebytes Anti-Malware version 1.75.0.1300
Plus les anciens outils de désinsfection JRT,Adwcleaner
IMPORTANT Désactivez vos protections (
Antivirus par-feu Spybot )
- Cliquez sur l'icône ZHPFix,présent sur votre Bureau
pour vista/W7/W8 clique-droit > exécuter en tant qu'administrateur
- Surlignez tout le texte ci-dessous puis cliquez droit Copier
Script ZHPFix
C:\extensions\Program Files (x86)\LyricsSeeker\131.xpi (.not file.)
C:\Users\Ahmed\AppData\Roaming\Azureus
C:\Users\Ahmed\AppData\Roaming\Bonanza
C:\Windows\Installer\5058c5c.msi
C:\Users\Ahmed\AppData\Roaming\UpdateBonanza
C:\Users\Ahmed\AppData\Roaming\uTorrent
M2 - MFEP: RegExtension {0ce6ac61-48e9-426f-9268-6f1e8ece06da} . (...) -- C:\Program Files (x86)\LyricsSeeker\131.xpi (.not file.)
M2 - MFEP: Extension [Ahmed - u0ej7ey1.default] {fa2d6af7-0818-4168-aab2-41ca9ed02a61}
R0 - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Start Page = http://speedial.com
R0 - HKLM\SOFTWARE\Wow6432Node\Microsoft\Internet Explorer\Main,Start Page = http://speedial.com
R5 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,ProxyOverride = <local>127.0.0.1;localhost;10.*;192.168.*;127.0.0.1:895;127.0.0.1:896
R5 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,ProxyServer = http=127.0.0.1:8118;https=127.0.0.1:8118
R5 - HKLM\Software\Microsoft\Windows\CurrentVersion\Internet Settings,ProxyOverride = <-loopback>
R5 - HKLM\Software\Microsoft\Windows\CurrentVersion\Internet Settings,ProxyServer = http=127.0.0.1:8877;https=127.0.0.1:8877
O2 - BHO: ?????????@Mail.Ru [64Bits] - {8984B388-A5BB-4DF7-B274-77B879E179DB} Clé orpheline
O2 - BHO: MSS+ Identifier [64Bits] - {0E8A89AD-95D7-40EB-8D9D-083EF7066A01} . (.McAfee, Inc. - Quick Browser Identifier for MSS+ Tool.) -- C:\Program Files\McAfee Security Scan\3.8.141\McAfeeMSS_IE.dll
O3 - Toolbar\WebBrowser: (no name) - [HKCU]{2318C2B1-4965-11D4-9B18-009027A5CD4F} Clé orpheline
O4 - HKLM\..\Wow6432Node\Run: [WsmUpdater] . (.Web Solution Mart - Updater.) -- C:\Program Files (x86)\Web Solution Mart\Fake Webcam Codecs Pack\Updater.exe
O23 - Service: twdns (twdns) . (...) - C:\Windows\SysWOW64\dns\bin\named.exe
O23 - Service: Hotspot Shield Service (hshld) . (.AnchorFree Inc. - Hotspot Shield 3.42.) - C:\Program Files (x86)\Hotspot Shield\bin\cmw_srv.exe
O23 - Service: Hotspot Shield Monitoring Service (HssWd) . (...) - C:\Program Files (x86)\Hotspot Shield\bin\hsswd.exe
O42 - Logiciel: McAfee Security Scan Plus - (.McAfee, Inc..) [HKLM][64Bits] -- McAfee Security Scan
O42 - Logiciel: Updater - (.Creative Island Media, LLC.) [HKLM][64Bits] -- {D54E3D9F-FEB8-4D2D-A138-B69A5C80080B}
O42 - Logiciel: Hotspot Shield 3.42 - (.AnchorFree Inc..) [HKLM][64Bits] -- HotspotShield
O43 - CFD: 09/06/2014 - 17:01:52 - [] ----D C:\Program Files (x86)\ChrisPC Free Anonymous Proxy
O43 - CFD: 01/09/2013 - 12:48:05 - [] ----D C:\Program Files (x86)\Common Files\Symantec Shared
O43 - CFD: 23/12/2013 - 01:36:47 - [] ----D C:\ProgramData\McAfee
O43 - CFD: 27/11/2014 - 08:38:55 - [] ----D C:\ProgramData\McAfee Security Scan
O43 - CFD: 01/09/2013 - 13:07:54 - [] ----D C:\ProgramData\Norton
O43 - CFD: 01/09/2013 - 12:44:11 - [] ----D C:\ProgramData\NortonInstaller
O43 - CFD: 01/09/2013 - 13:07:53 - [] ----D C:\ProgramData\Symantec
O43 - CFD: 15/02/2014 - 08:20:46 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\McAfee Security Scan Plus
O43 - CFD: 30/12/2013 - 00:07:17 - [] ----D C:\Users\Ahmed\AppData\Roaming\Bonanza
O43 - CFD: 08/02/2014 - 06:07:15 - [] ----D C:\Users\Ahmed\AppData\Roaming\UpdateBonanza
O43 - CFD: 20/09/2014 - 19:26:24 - [] ----D C:\ProgramData\Hotspot Shield
O43 - CFD: 20/09/2014 - 19:23:53 - [] ----D C:\Users\Ahmed\AppData\Roaming\Hotspot Shield
O43 - CFD: 17/05/2014 - 18:29:32 - [] ----D C:\Users\Ahmed\AppData\Roaming\uTorrent
O43 - CFD: 20/09/2014 - 19:26:25 - [] ----D C:\Program Files (x86)\Hotspot Shield
O43 - CFD: 20/09/2014 - 19:24:34 - [] ----D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Hotspot Shield
O69 - SBI: SearchScopes [HKUS\.DEFAULT] {006ee092-9658-4fd6-bd8e-a21a348e59f5} - (Web Search) - http://feed.snapdo.com
O69 - SBI: SearchScopes [HKUS\S-1-5-18] {006ee092-9658-4fd6-bd8e-a21a348e59f5} - (Web Search) - http://feed.snapdo.com
[MD5.238F06F0151652B032D4DC2B54C74EB3] [WIS][06/02/2014] (.LPT - LPT System Updater Service.) -- C:\Windows\Installer\5058c5c.msi [1712128]
[MD5.00000000000000000000000000000000] [APT] [RealDownloaderDownloaderScheduledTaskS-1-5-21-735007629-4261386-1335072915-1000] (...) -- C:\Program Files (x86)\RealNetworks\RealDownloader\recordingmanager.exe (.not file.)
[MD5.00000000000000000000000000000000] [APT] [RealDownloaderRealUpgradeLogonTaskS-1-5-21-735007629-4261386-1335072915-1000] (...) -- C:\Program Files (x86)\RealNetworks\RealDownloader\realupgrade.exe (.not file.)
[MD5.00000000000000000000000000000000] [APT] [RealDownloaderRealUpgradeScheduledTaskS-1-5-21-735007629-4261386-1335072915-1000] (...) -- C:\Program Files (x86)\RealNetworks\RealDownloader\realupgrade.exe (.not file.)
[MD5.00000000000000000000000000000000] [APT] [{69416A2B-59CE-4E65-8C6F-C87C8D86559D}] (...) -- C:\Users\Ahmed\AppData\Roaming\iPumper\ipumperinst.exe (.not file.)
[MD5.00000000000000000000000000000000] [APT] [{94E5EA7E-7BEC-48EA-AD04-BC66E2210A39}] (...) -- C:\Users\Ahmed\Downloads\Windows_Movie_Maker_2.0.exe (.not file.)
[MD5.00000000000000000000000000000000] [APT] [{D606987E-9851-4B2B-9525-3A75EE622399}] (...) -- C:\Users\Ahmed\Downloads\wlsetup-web.exe (.not file.)
[MD5.E2017AAE1583DA85744FD9DE324C3A76] - (...) -- C:\Windows\SysWOW64\dns\bin\named.exe [233472] [PID.4052]
[MD5.77ED10C64F9DE2BF3F4F0B92541422F6] - (.AnchorFree Inc. - Hotspot Shield 3.42.) -- C:\Program Files (x86)\Hotspot Shield\bin\cmw_srv.exe [919040] [PID.2244]
HKLM\SOFTWARE\Microsoft\Tracing\Azureus_RASAPI32
HKLM\SOFTWARE\Microsoft\Tracing\Azureus_RASMANCS
HKLM\SOFTWARE\Microsoft\Tracing\BackupStack_RASAPI32
HKLM\SOFTWARE\Microsoft\Tracing\BackupStack_RASMANCS
HKLM\SOFTWARE\Microsoft\Tracing\updateWebConnect_RASAPI32
HKLM\SOFTWARE\Microsoft\Tracing\updateWebConnect_RASMANCS
HKLM\SOFTWARE\Microsoft\Tracing\Vuze_4900_Installer64_RASAPI32
HKLM\SOFTWARE\Microsoft\Tracing\Vuze_4900_Installer64_RASMANCS
HKLM\SOFTWARE\Wow6432Node\Microsoft\Tracing\InternetUpdaterService_RASAPI32
HKLM\SOFTWARE\Wow6432Node\Microsoft\Tracing\InternetUpdaterService_RASMANCS
HKLM\SOFTWARE\Wow6432Node\Microsoft\Tracing\uTorrent_RASAPI32
[HKCU\Software\Bonanza]
[HKLM\Software\Wow6432Node\aducky]
[HKLM\Software\Wow6432Node\McAfee.com]
[HKLM\Software\Wow6432Node\McAfeeInstaller]
[HKCU\Software\MCAFEE]
[HKLM\Software\Wow6432Node\mcafeeupdater]
[HKLM\Software\mcafeeupdater]
[HKLM\Software\Wow6432Node\ChrisPC Free Anonymous Proxy]
[HKLM\Software\Wow6432Node\Chrispc]
[HKLM\Software\Wow6432Node\685D6D1C-D73A-4F37-B7E5E53660311DDB]
SS - | Demand 16/01/2014 289256 | (McComponentHostService) . (.McAfee, Inc..) - C:\Program Files\McAfee Security Scan\3.8.141\McCHSvc.exe
SR - | Auto 10/07/1658 0 | (twdns) . (...) - C:\Windows\system32\dns\bin\named.exe
SS - | Demand 17/05/2014 78512 | (HssTrayService) . (...) - C:\Program Files (x86)\Hotspot Shield\bin\HssTrayService.exe
SS - | Auto 16/05/2014 430344 | (HssWd) . (...) - C:\Program Files (x86)\Hotspot Shield\bin\hsswd.exe
SR - | Auto 17/05/2014 919040 | (hshld) . (.AnchorFree Inc..) - C:\Program Files (x86)\Hotspot Shield\bin\cmw_srv.exe
PROXYFix
EmptyPrefetch
ShortcutFix
EmptyCLSID
FirewallRaz
EmptyTemp
EmptyFlash
Sysrestore
- Fermez toutes les applications en cours (notamment votre navigateur)
Dans l'interface de ZHPFix Cliquez sur Importer et sur OK
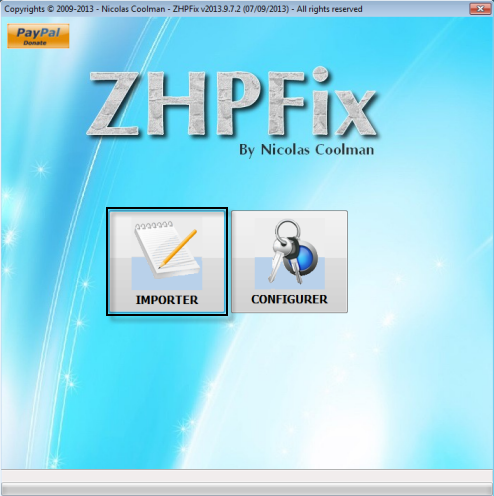
Attention :vérifiez que que toutes les lignes se sont collées
- Puis Cliquez sur "GO"
- Confirmez les nettoyages des données en cliquant sur "Oui"

Le nettoyage s'effectue, ne touchez à rien pendant cette étape, si le programme demande un redémarrage du pc > faites le !
- Une fois le scan terminé le fichier ZHPFixReport à été crée sur le bureau.
- Hébergez le rapport ZHPFixReport sur le site
puis copier/coller le lien fourni dans votre prochaine réponse.
Télécharges Adwcleaner (de Xplode) sur ton Bureau
Désactivez vos protections: antivirus, ... Ferme toutes les applications en cours (notamment votre navigateur)
Fais clique droit dessus, exécuter en tant qu'administrateur sous Windows : 7/8 et Vista
- Cliquez sur oui pour Accepter la licence

- Choisir l'option Scanner
- Acceptez l'avertissement en cliquant sur OK
- Hébergez le contenu du rapport qui apparaît au redémarrage du PC sur le site
Puis copie/colle le lien fourni dans votre prochaine réponse.
Pas de réponse sujet supprimé de mes suivis





